
Shell & File Operations
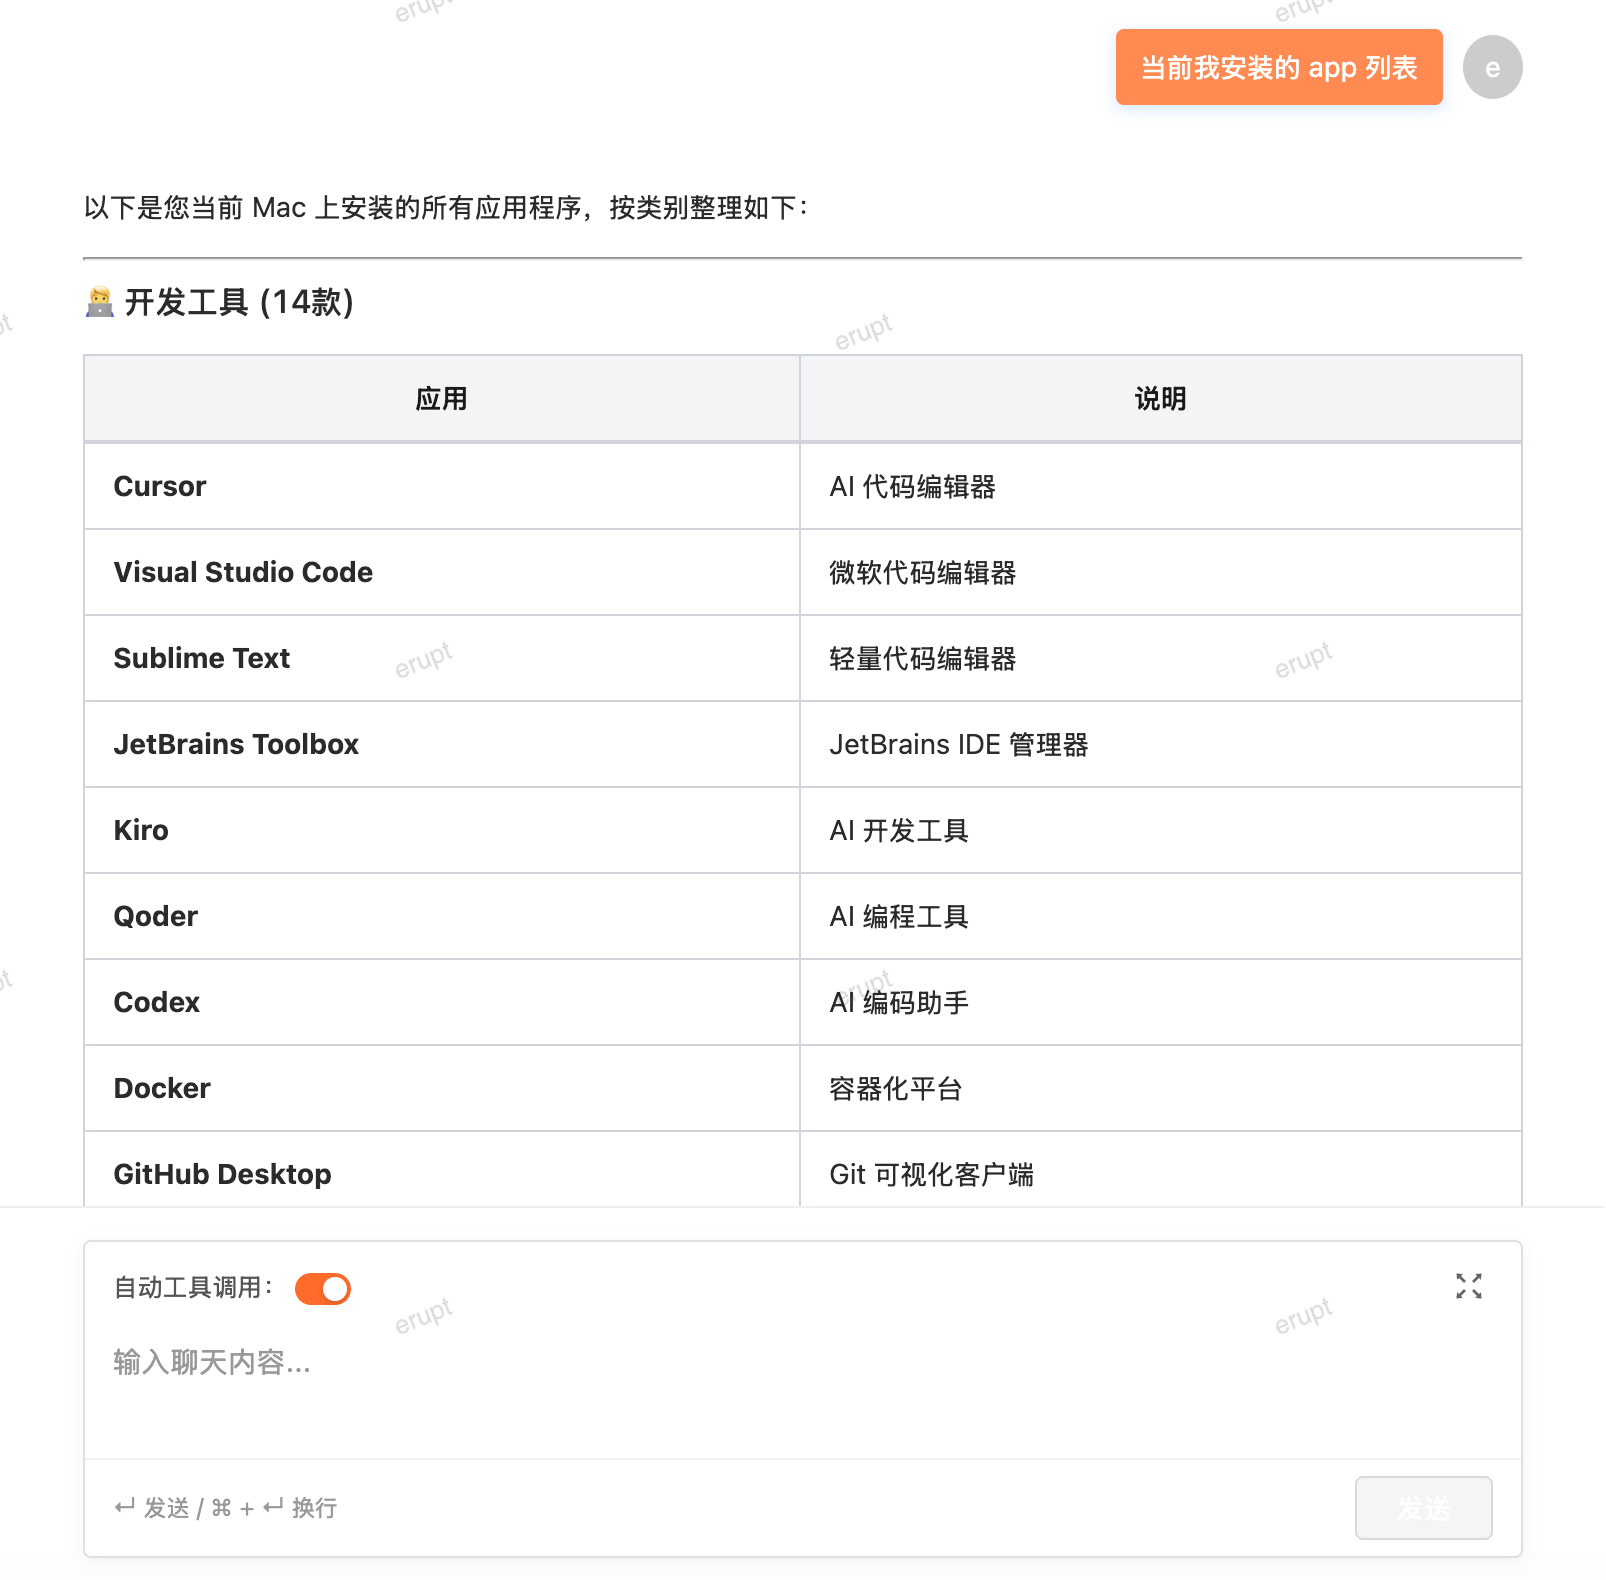
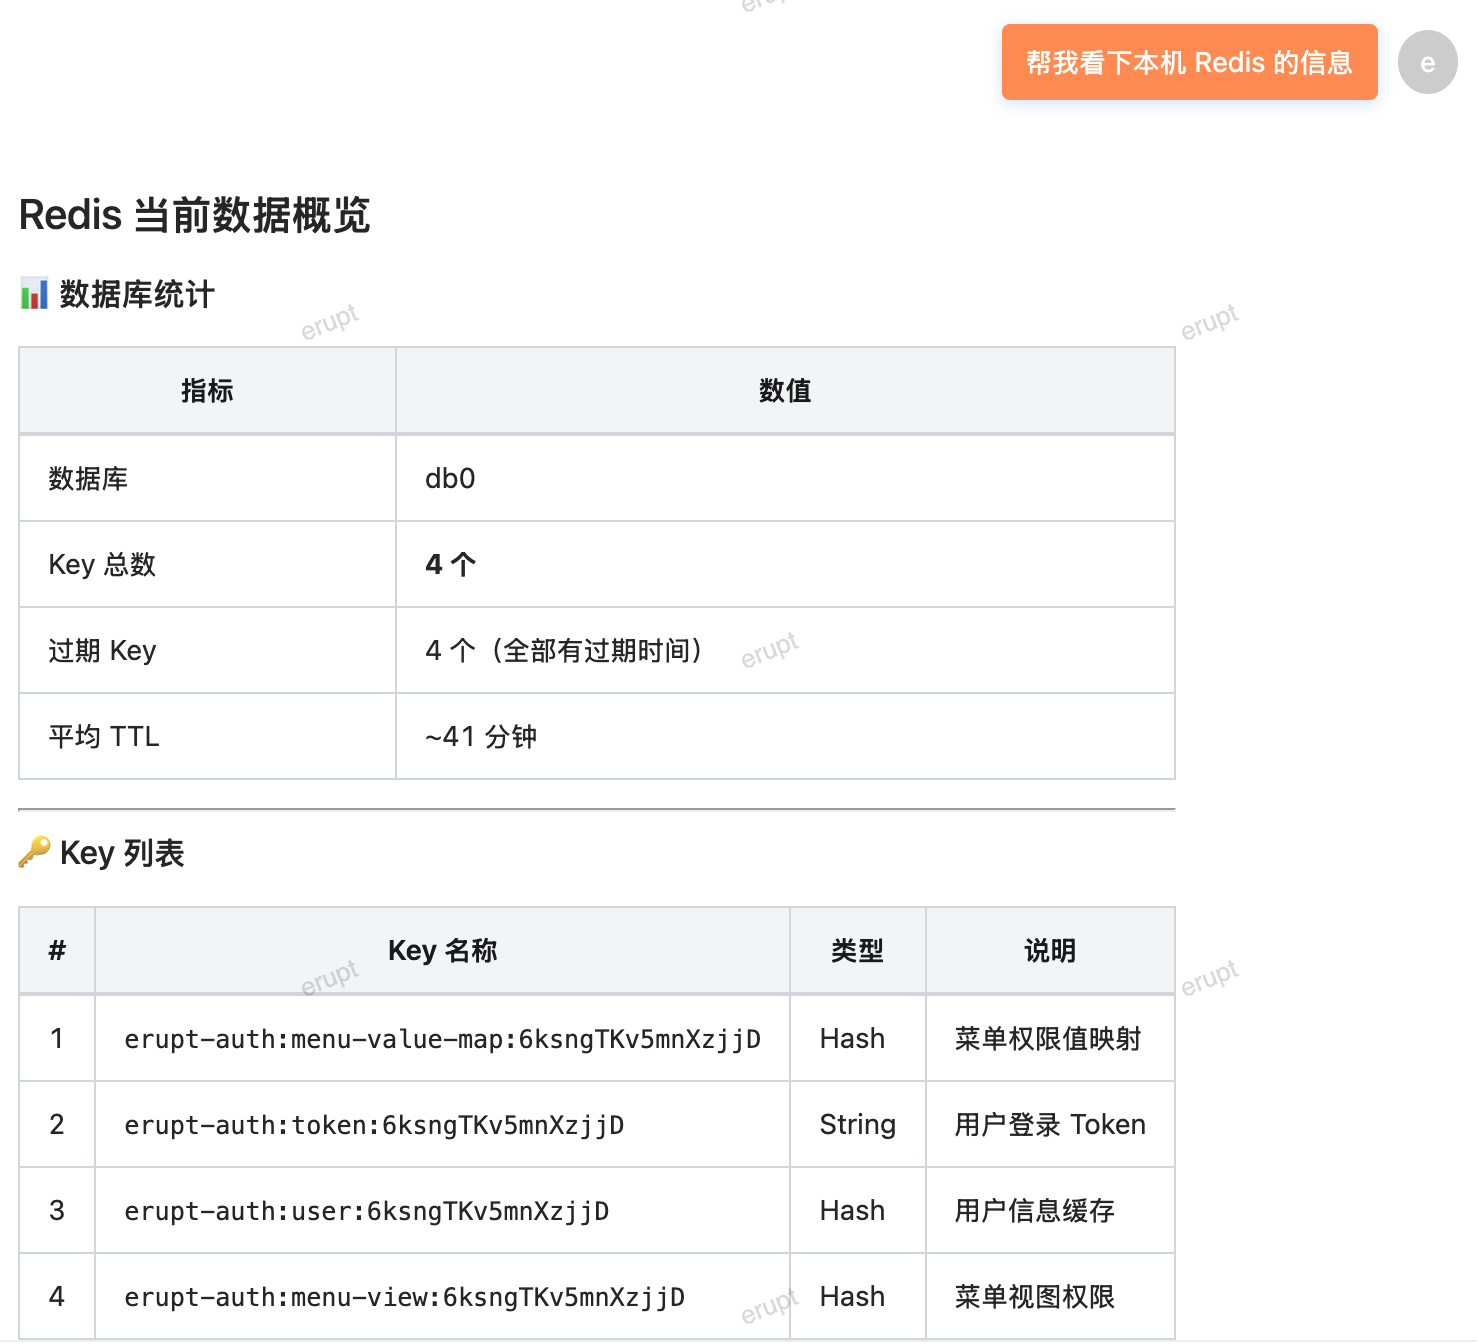
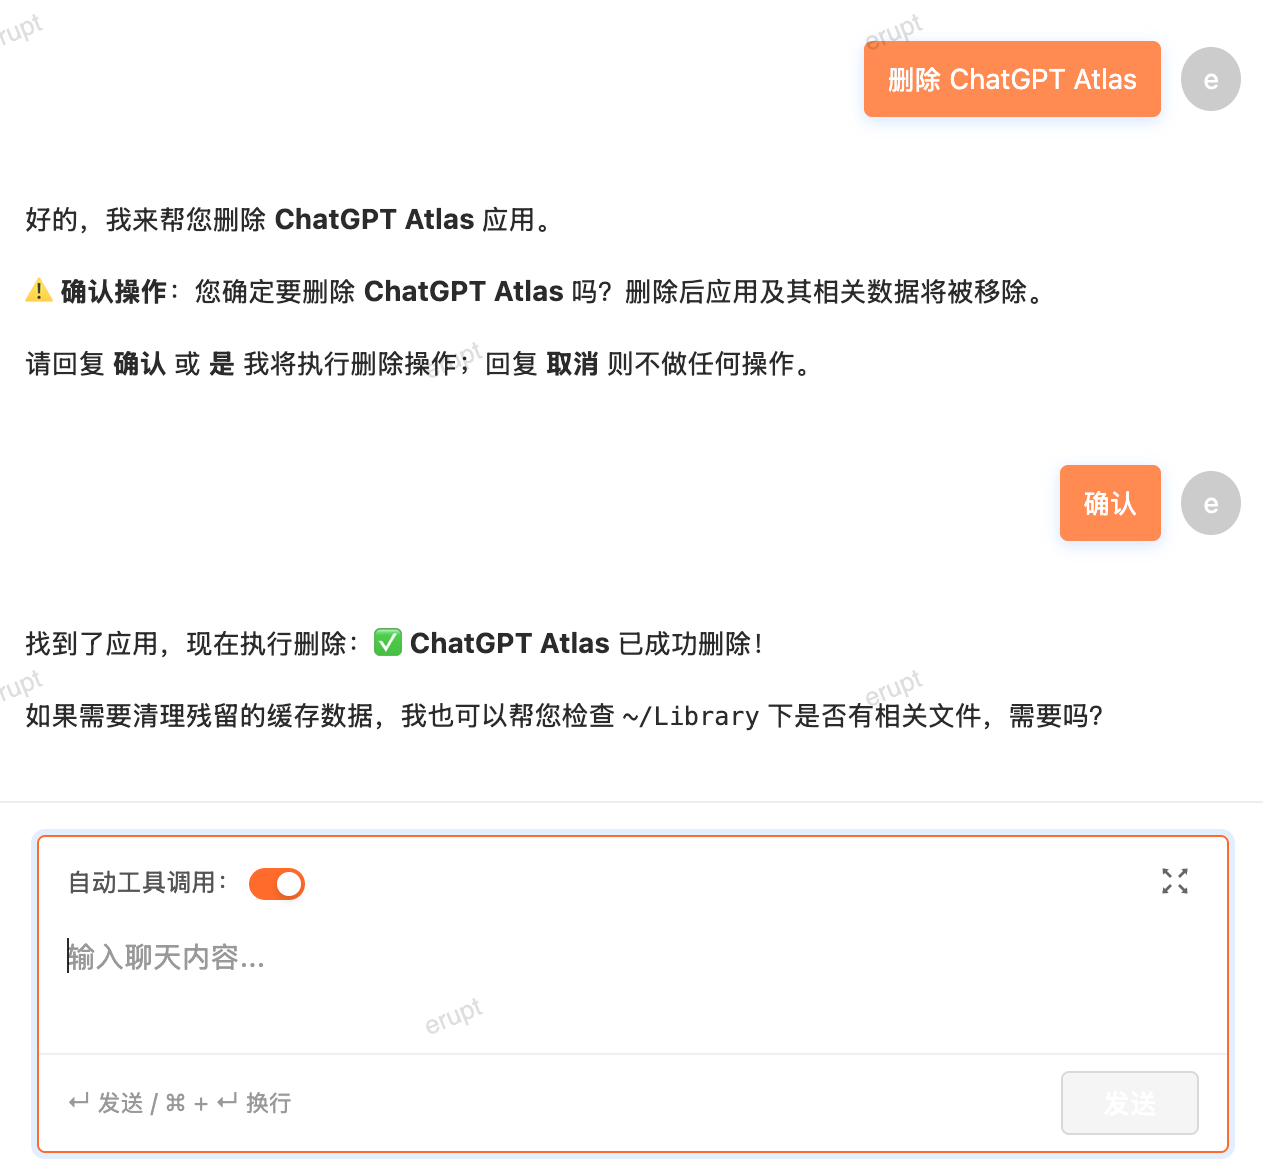
Shell Execution Guardrails
execShell is off by default and must be enabled explicitly with erupt.ai.claw.enable-exec-shell: true; granting it to the admin role only is recommended. Even when enabled, several guardrails apply in order:
- Hardline deny list: catastrophic commands like
rm -rf /, fork bombs,mkfs, shutdown/reboot, and raw device writes are always blocked and cannot be configured away; - Directory sandbox: commands are anchored to the current user's sandbox
~/.erupt/{account}; other directories must be allowlisted viaerupt.ai.claw.shell-allowed-paths; - Sensitive env stripping: environment variables whose names contain KEY / TOKEN / SECRET / PASSWORD etc. are not inherited by the child process;
- Output truncation: output is capped at 64KB per command, with a 600-second max timeout (default 30 seconds).
The file tools (readFile / writeFile and friends) are confined to the same sandbox directory; see the full @Tools Reference Table.
Contributors
 YuePeng
 Claude Opus 5 (1M context)